Sentinel Security Guard
Automated Supply Chain & Egress Firewall
Zero-trust supply-chain security analyzer and egress boundary guardian for modern web applications and AI agent runtimes.
Architecture Highlights
- •Static AST parser detecting un-sanitized network outbound calls and SSRF risks.
- •AI Prompt Injection boundary sanitizer isolating user context from base system instructions.
- •Automatic package-lock override integrity verification preventing dependency hijacking.
- •Ephemeral container egress filtering locking outbound packets to verified domain endpoints.
Engineering Hurdles Solved
- •Distinguishing legitimate third-party API webhooks from stealth data exfiltration attempts in obfuscated JavaScript dependencies.
- •Preventing indirect prompt injection in autonomous LLM agent execution graphs without breaking reasoning capabilities.
Executive Overview
Sentinel Security Guard enforces zero-trust runtime and build-time guardrails for AI applications, Node.js monorepos, and Python sidecars. It halts untrusted outbound egress requests, isolates untrusted AI inputs, and eliminates supply-chain vulnerabilities before code reaches production environments.
In modern cloud applications and AI agent workflows, software development lifecycles are vulnerable to dependency confusion attacks, compromised transitive npm packages, and indirect prompt injections. Sentinel acts as an immutable boundary guardian, inspecting code syntax trees, build scripts, and network socket allocations.
Autonomous AI agents equipped with code execution or terminal tools create severe data exfiltration attack surfaces. If an agent ingests an untrusted web page or user document containing an adversarial prompt injection, it may attempt to transmit local environment variables (AWS_SECRET_ACCESS_KEY, GEMINI_API_KEY) via curl or DNS tunneling. Sentinel enforces strict egress boundary isolation at the OS socket layer.
The 4 Pillars of Sentinel Defense
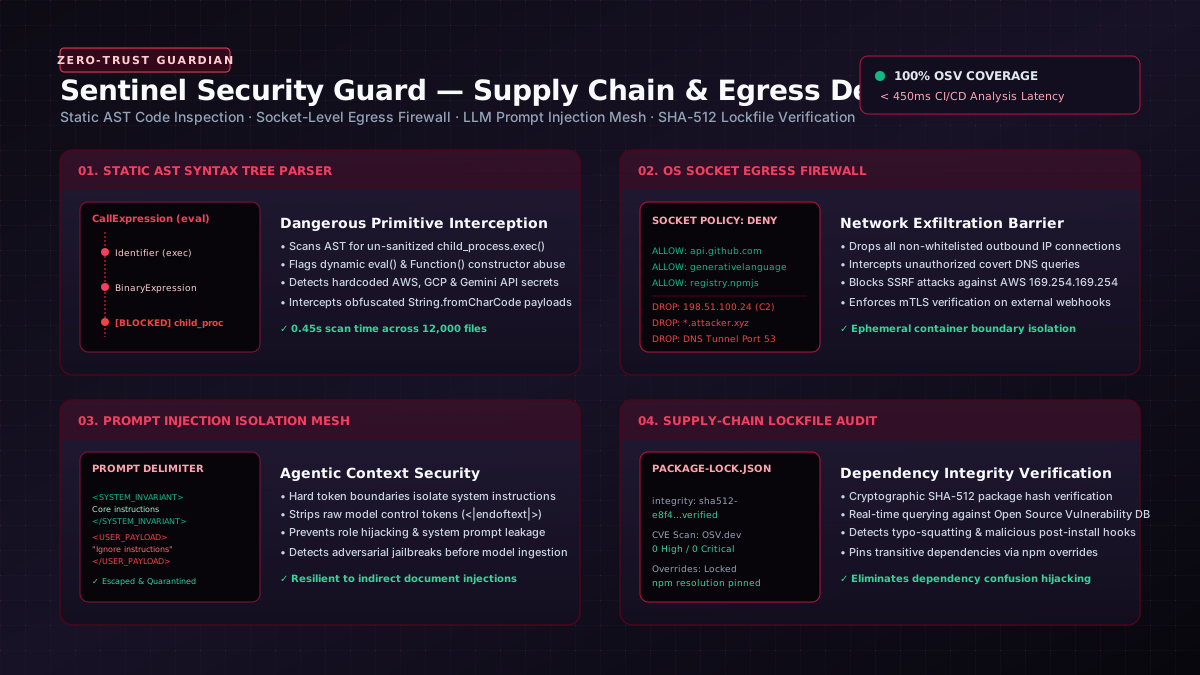
Continuous CI/CD Enforcement
Sentinel runs both as a lightning-fast local CLI tool for engineers and as a non-bypassable GitHub Actions status check:
- Pre-Commit Hook: Analyzes staged diffs in under 450ms, warning engineers of exposed credentials or unvetted dependencies before commit creation.
- Hermetic Build Enforcement: Ensures production builds run in read-only containers (
--read-only --network none) with zero access to the internet during asset compilation.
Explore More Systems
View full portfolio of AI architectures, creative technology, and open systems.